GIDS news media, articles, insights and virtual events educate and illuminate its audiences so they can be fully prepared to deal with the new realities at work and in their professions.
Contain the Blast Radius of AI-Accelerated Attacks
Fri, April 30Reliability, Observability & SecurityPlatform Engineering & DevOpsAI-Native Software
AI-assisted offensive tools can accelerate reconnaissance, vulnerability discovery, and attack chaining. At the same time, AI applications create new paths through retrieved content, prompts, tools, workload identities, APIs, and enterprise data. A compromised instruction or over-privileged tool can therefore travel well beyond the original application boundary.
In this session, you will explore a containment-first architecture for reducing that blast radius. Following a representative attack path from malicious retrieved content through an attempted tool action and lateral movement, you will examine how threat boundaries, least-privilege identities, tool permission matrices, workload segmentation, protected data surfaces, pipeline checks, and capability-specific stop controls can interrupt the chain. You will also see how AI-specific risks such as indirect prompt injection, retrieval poisoning, and excessive agency connect with familiar security failures, and how detection, isolation, and restoration can be handled when preventive controls are not enough.
What You Will Learn
How to map an attack path across prompts, retrieval, tools, identities, workloads, APIs, and data
How to apply least authority and segmentation to prevent a compromised capability from spreading
How to define detection, isolation, and restoration evidence for an AI-related security incident
Who Should Attend
Security Engineers, Software and Enterprise Architects, Platform Engineers, DevSecOps Leads, and Technical Leaders responsible for AI-enabled systems. Working knowledge of application security, cloud identity, and AI agent or RAG architecture is recommended.
Director of Architecture, Expert in Cloud-native Solutions
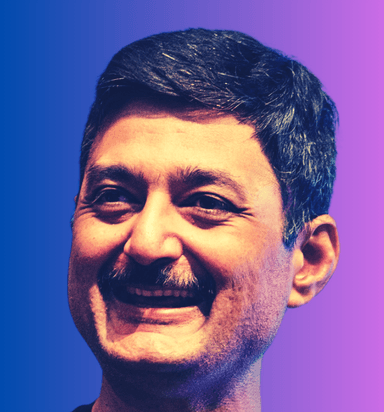
Rohit Bhardwaj is a Director of Architecture working at Salesforce. Rohit has extensive experience architecting multi-tenant cloud-native solutions in Resilient Microservices Service-Oriented architectures using AWS Stack. In addition, Rohit has a proven ability in designing solutions and executing and delivering transformational programs that reduce costs and increase efficiencies.
As a trusted advisor, leader, and collaborator, Rohit applies problem resolution, analytical, and operational skills to all initiatives and develops strategic requirements and solution analysis through all stages of the project life cycle and product readiness to execution. Rohit excels in designing scalable cloud microservice architectures using Spring Boot and Netflix OSS technologies using AWS and Google clouds. As a Security Ninja, Rohit looks for ways to resolve application security vulnerabilities using ethical hacking and threat modeling. Rohit is excited about architecting cloud technologies using Dockers, REDIS, NGINX, RightScale, RabbitMQ, Apigee, Azul Zing, Actuate BIRT reporting, Chef, Splunk, Rest-Assured, SoapUI, Dynatrace, and EnterpriseDB. In addition, Rohit has developed lambda architecture solutions using Apache Spark, Cassandra, and Camel for real-time analytics and integration projects.
Rohit has done MBA from Babson College in Corporate Entrepreneurship, Masters in Computer Science from Boston University and Harvard University. Rohit is a regular speaker at No Fluff Just Stuff, UberConf, RichWeb, GIDS, and other international conferences.